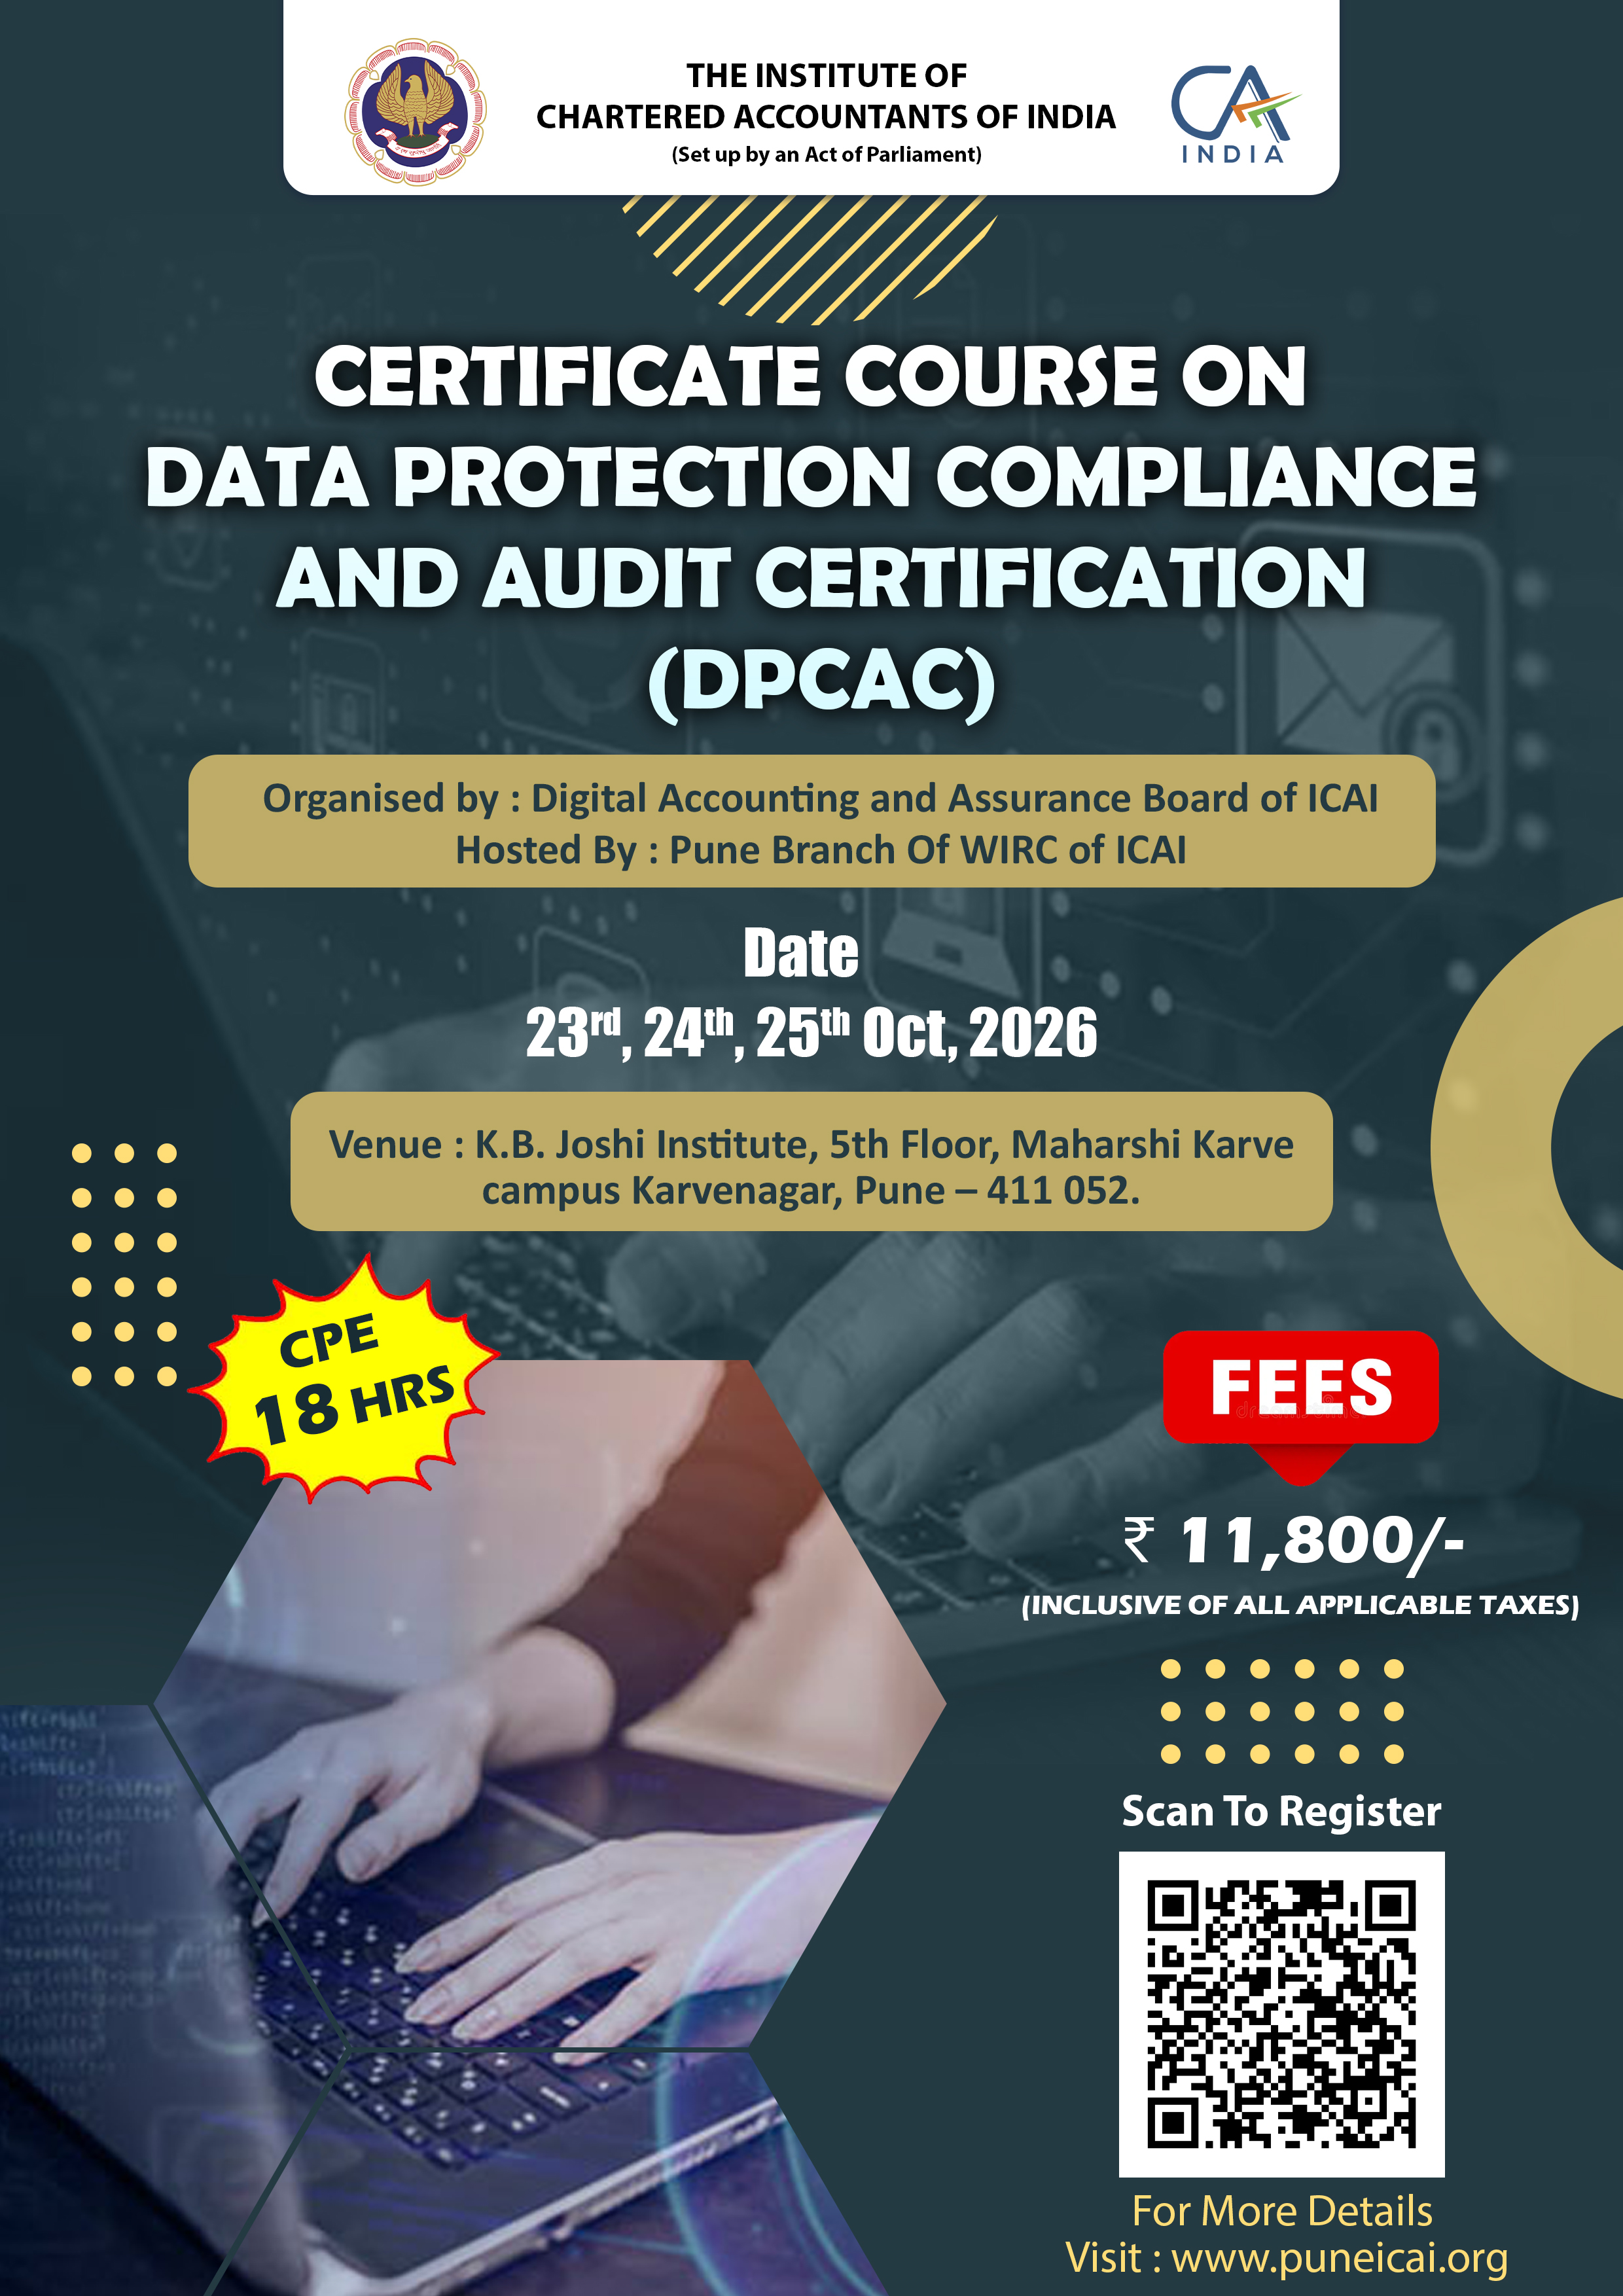
Event Start Date : 23-Oct-2026 09:00 AM
Event End Date : 25-Oct-2026 06:00 PM
Event Cut Off Date : 22-Oct-2026 06:00 PM
Event Time : 09:00 AM To 06:00 PM
Event Venue : K.B. Joshi Institute of Information Technology Rama Purushottam Vidya Sankul, 5th Floor, Maharshi Karve campus Karvenagar, Pune – 411 052.
Event Fee : ₹11800
Certificate Course on Data Protection Compliance and Audit Certification (DPCAC)
under Digital Accounting and Assurance Board of ICAI!!
Hosted By : Pune Branch of WIRC of ICAI
Venue : K.B. Joshi Institute of Information Technology Rama Purushottam Vidya Sankul,
5th Floor, Maharshi Karve campus Karvenagar, Pune – 411 052.
Please click the link below to complete your registration.
https://learning.icai.org/committee/daab/dpcac/pune-2026/batch-24/
Date & Duration : (3Days )
23rd , 24th, 25th Oct, 2026
Registration Fees : 10000 Plus GST Batch Limit : 50 CPE Hours: 18 Structured
Programme Structure :
Daily Session Structure
|
Session 1 & 2 |
Session 3 |
Session 4 |
|
|
Theory (Pre-Lunch) |
Use Case (Post-Lunch) |
Activity (Post-Lunch) |
Wrap-Up |
|
Time |
Session |
Topic / Module |
Type |
|
10:00 – 11:30 |
Session 1 |
Module 1: Foundations of Data Privacy and Digital Personal Data Protection Understanding Digital Personal Data; Global Principles (OECD & GDPR); Evolution of Privacy Laws Globally and in India; Constitutional Basis – K.S. Puttaswamy v. Union of India; IT Act 2000 & Privacy; Threats & Risks to Personal Data in Digital Form; Overview of International Data Protection Laws (GDPR, Singapore PDPA etc.) |
Concepts |
|
11:30 – 11:45 |
|
☕ Tea Break |
|
|
11:45 – 01:15 |
Session 2 |
Module 2: DPDPA 2023 – Scope, Rights and Duties Applicability, Scope, Exclusions & Exemptions; Lawful Basis of Processing; DPDPA Rules & Regulations; Definitions & Roles – Data Principal, Data Fiduciary, Significant Data Fiduciary, Data Processor; Rights & Duties of Data Principal; Obligations of Data Fiduciary & Processor; Children’s Data; Data Protection Compliance Requirements; Cross-border Transfer & Data Localisation; Penalties & Adjudication; Audit Considerations |
Concepts |
|
01:15 – 02:00 |
|
🍽️ Lunch Break |
|
|
02:00 – 03:30 |
Session 3 |
Use Case: Analysing a MSME Data Breach Under DPDPA Scenario-based exercise applying Module 1 & 2 – Identifying data principal rights violations in a breach scenario; assessing lawful basis of processing; mapping roles (Data Fiduciary, Processor, Significant Data Fiduciary); evaluating penalties under DPDPA; comparing DPDPA vs. GDPR obligations in a cross-border breach; recommending remedial actions |
Application |
|
03:30 – 03:45 |
|
☕ Tea Break |
|
|
03:45 – 05:15 |
Session 4 |
Group Discussion: Privacy as a Fundamental Right – Balancing Individual Rights with Organisational Obligations Under Moderator Observation Groups deliberate on: the impact of DPDPA on digital privacy practices; tensions between data principal rights and business needs of data fiduciaries; effectiveness of DPDPA’s penalty framework as a deterrent; comparison with GDPR enforcement – lessons for India
|
Group Discussion |
|
05:15 – 05:30 |
|
Day 1 Wrap-Up & Reflections |
|
|
Time |
Session |
Topic / Module |
Type |
|
10:00 – 11:30 |
Session 5 |
Module 3: Data Life Cycle Management Personal Data Collection – What Can Be Collected, Data Minimisation at Source; Data Discovery & Classification; Collection of Personal Data Classification & Recording; Personal Data Inventory Management & Ownership; Use & Processing – Limitation, Accuracy; Storage & Retention; Sharing with Data Processors & Other Data Fiduciaries; Update & Correction; Erasure & Destruction; Grievance Redressal & Review; ROPA, Incident Logs, Audit Logs; Documentation & Record-Keeping; Audit Considerations |
Concepts |
|
11:30 – 11:45 |
|
☕ Tea Break |
|
|
11:45 – 01:15 |
Session 6 |
Module 4: Governance and Organisational Measures Data Protection Board of India – Role, Powers & Duties; Entity-Level Governing Body Roles & Responsibilities; Data Privacy & Protection Policies & Procedures; DPO Roles & Responsibilities; Grievance Redressal Mechanism & Transparency; Training & Awareness Programmes; Data Processor & Third Party Management & Due Diligence; Periodic Risk Assessments & DPIA (SDF); Incident Response & Data Breach Reporting; Internal Audit & Compliance Reviews; Statutory Data Audits |
Concepts |
|
01:15 – 02:00 |
|
🍽️ Lunch Break |
|
|
02:00 – 03:30 |
Session 7 |
Use Case: Building a Data Life Cycle & Governance Framework for an Organisation Hands-on exercise applying Modules 3 & 4 – Mapping a data life cycle for a sample organisation; creating a personal data inventory; defining data classification schema; designing data retention & erasure policies; establishing governance structure with DPO, grievance redressal, and incident response procedures; preparing a ROPA template; conducting a mock DPIA |
Applicatio |
|
03:30 – 03:45 |
|
☕ Tea Break |
|
|
03:45 – 05:15 |
Session 8 |
Panel Discussion: Implementing Data Governance in Practice – Challenges Across Industries Group Representatives as Panellists Panel 1: Data Life Cycle Challenges, real-world issues in data inventory, minimisation, cross-border sharing, retention and destruction across sectors (BFSI, Healthcare, IT/ITES) Panel 2: Governance & Organisational Readiness, DPO effectiveness, board-level accountability, third-party risk management, balancing compliance costs with business agility |
Panel Discussion |
|
05:15 – 05:30 |
|
Day 2 Wrap-Up & Reflections |
|
DAY 3 — Consent, Technical Measures, Compliance & Audit (Modules 5, 6, 7 + Professional Practice)
|
Time |
Session |
Topic / Module |
Type |
|
10:00 – 11:30 |
Session 9 |
Module 5: Notice and Consent Management & Module 6: Technical Measures for Digital Data Protection Module 5 – Valid Notice & Consent under DPDP; Consent Modification, Withdrawal, Retention, Erasure & Disclosure; Deemed Consent; Pre-Act Data; Structure & Elements of Notice; Consent Management Architecture & Life Cycle; Consent Managers – Registration & Responsibilities; Compliance & Audit Requirements Module 6 – IT Architecture & Information Security Framework; Encryption & Access Control; Anonymization & Pseudonymization; Secure Logging & Audit Trails; Data Backup & Recovery; Endpoint Security; Secure Disposal; Legality of Cookies; Data Breach Incident Response |
Concepts |
|
11:30 – 11:45 |
|
☕ Tea Break |
|
|
11:45 – 01:15 |
Session 10 |
Module 7: DPDP Compliance and Audit & Professional Areas of Practice Module 7 – DPDPA Compliance Monitoring & Audit; Planning & Performance of Data Audits; Privacy Governance Framework Effectiveness; Data Protection Impact Assessment; Breach Risk Assessment; Audit of Compliance with DPDPA Provisions; Technical & Organisational Measures Effectiveness; Consent Architecture Audit; Grievance Redressal Effectiveness; Data Sharing Controls; Breach Reporting Mechanisms Professional Practice. Advisory for Data Privacy Implementation & Compliance; Monitoring Support; Internal Data Privacy & Protection Audits; Virtual DPO Services; External Data Audits; Alternate Dispute |
Concepts |
|
|
|
Resolution; Representation before Data Protection Board; Impact on Other Types of Audit |
|
|
01:15 – 02:00 |
|
🍽️ Lunch Break |
|
|
02:00 – 03:30 |
Session 11 |
Use Case: End-to-End DPDPA Compliance Audit & Advisory Engagement Comprehensive exercise applying Modules 5, 6, 7 & Professional Practice. Evaluating an organisation’s consent architecture; reviewing technical safeguards (encryption, access controls, audit trails); conducting a mock DPDPA compliance audit; performing breach risk assessment; preparing audit findings & remediation report; advising as a Virtual DPO on corrective measures |
Application |
|
03:30 – 03:45 |
|
☕ Tea Break |
|
|
03:45 – 05:15 |
Session 12 |
Capstone Project Presentation with Individual Viva Voce Individual Viva by Faculty Each participant shares a capstone project demonstrating end-to-end DPDPA readiness for a given organisation through google form, covering consent framework design, technical security measures, compliance audit plan, professional advisory recommendations, and breach response protocol. Followed by individual viva voce examination. |
Capstone + Viva |
|
05:15 – 05:30 |
|
Valedictory & Certificate Distribution |
|
Day runs from 10:00 AM to 5:30 PM. Each session is 1.5 hours (90 minutes). Tea breaks are 15 minutes. Lunch break is 45 minutes. A 15-minute wrap-up slot closes each day.
Sessions 1 & 2 (pre-lunch) are dedicated exclusively to concepts. Post-lunch sessions are strictly application: Session 3 is always a hands-on use case exercise, and Session 4 is always a group activity. This ensures maximum engagement during the post-lunch period.
Day 1: Module 1 (Foundations of Data Privacy) and Module 2 (DPDPA 2023 – Scope, Rights & Duties). These establish the legal and conceptual foundation for the entire programme.
Day 2: Module 3 (Data Life Cycle Management) and Module 4 (Governance & Organisational Measures). These build on the legal framework with operational and governance perspectives.
Day 3: Module 5 (Notice & Consent) combined with Module 6 (Technical Measures) in Session 9, followed by Module 7 (Compliance & Audit) combined with Professional Areas of Practice in Session 10. Day 3 brings together the implementation and professional practice dimensions.
Day 1 Use Case: Analyses a cross-border personal data breach, applying the legal principles and DPDPA provisions from Modules 1 & 2.
Day 2 Use Case: Designs a data life cycle and governance framework, applying operational and organisational concepts from Modules 3 & 4.
Day 3 Use Case: Conducts an end-to-end DPDPA compliance audit and advisory engagement, applying consent, technical, audit, and professional practice concepts from Modules 5, 6, 7 and Professional Areas.
Day 1 – Group Discussion (Moderator-observed): Focuses on privacy as a fundamental right, the impact of the Puttaswamy judgement, data principal rights vs. organisational obligations, and DPDPA penalty effectiveness – all grounded in Module 1 & 2 topics.
Day 2 – Panel Discussion (Group Representatives): Two panels debate real-world challenges in data life cycle management and governance implementation across industries – directly applying Module 3 & 4 topics. Day 3 – Capstone Project with Individual Viva Voce: Each participant presents a comprehensive DPDPA readiness plan covering consent frameworks, technical safeguards, audit planning, and advisory recommendations – synthesising all Day 3 modules. Followed by individual viva examination.